Menu
ServicesProductsAboutContact

Home / Services / AppGate Professional Services
AppGate logoProfessional Services

Make your network invisible to attackers with AppGate Zero Trust

Trezbon designs, deploys and validates AppGate direct-routed ZTNA, so only verified users can even see your applications, on-premises, in the cloud and at the edge.

Request a ConsultationExplore Services
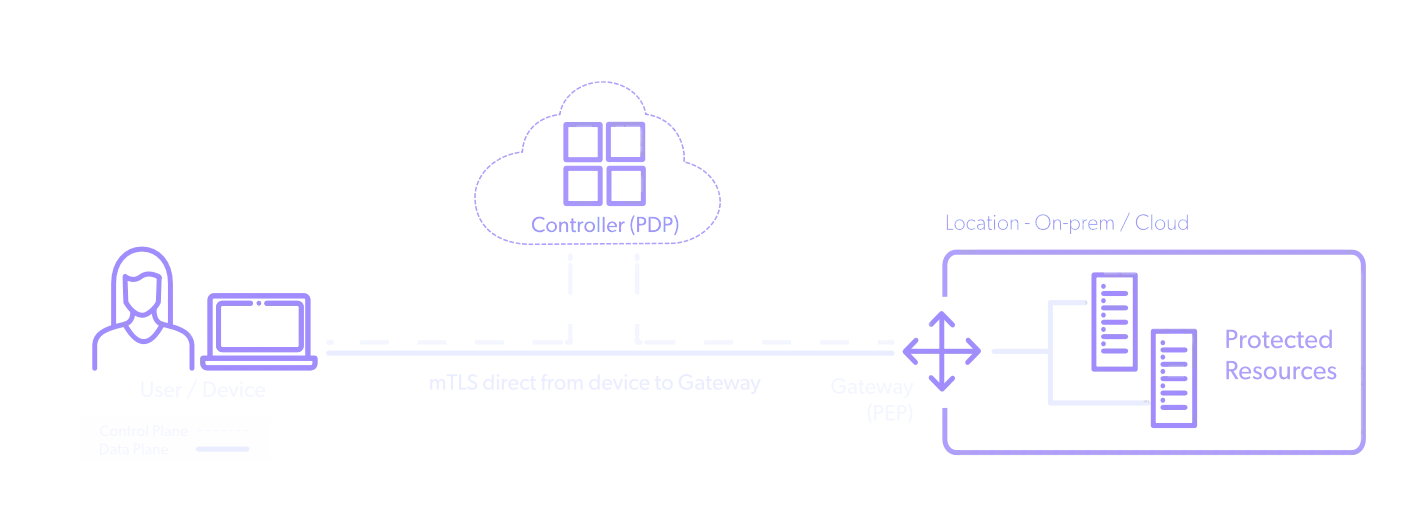
Direct-routed ZTNA model: user device connects by mTLS directly to the Gateway while the Controller makes access decisions and protected resources stay cloaked
Unauthorised scan: the Gateway gives no responseClient sends a single packet authorization knockController verifies identity, device and contextDirect mTLS tunnel opens to the GatewayResources appear for this verified user only
70+Countries with AppGate presence
600+Enterprise and government customers
8-10xPerformance vs cloud-routed, per AppGate
FIPS 140-3Plus NIAP and Common Criteria certified

Figures as published by AppGate. AppGate and the AppGate logo are trademarks of AppGate, Inc.

Why direct-routed ZTNA

Security that also makes access faster

Replace broad network access with identity-based, per-session access, without forcing traffic through someone else's cloud.

Cloak your environment

Resources stay invisible until a user is verified, shrinking the attack surface and blocking reconnaissance before it starts.

Direct-routed performance

Individual mTLS tunnels go straight to the Gateway, so on-premises traffic stays on your network and nothing hair-pins through a vendor cloud.

Sovereign control

Access decisions are made inside your own security boundary, with no dependency on an external cloud and support for air-gapped designs.

What we deliver

End-to-end AppGate professional services

One accountable team from Zero Trust design to a validated, cloaked environment.

01

Design

A Zero Trust access architecture built around your users, data and risk.

  • Access model for users, devices, workloads and OT/IoT
  • Data-centric policy design using metadata tags and labels
  • Controller (PDP) and Gateway (PEP) placement for on-premises, cloud and hybrid
  • Identity provider, MFA and device-posture integration
  • VPN migration plan, sizing and high availability
02

Implementation

Controlled deployment with minimal disruption to users.

  • Controller and Gateway deployment across your environments
  • SSO and identity integration with phased client rollout
  • VPN replacement with a parallel-run period
  • Policy as code and automation through APIs and DevSecOps pipelines
  • Server-initiated, branch, site-to-site and OT/IoT connectivity
03

Testing

Evidence that resources are cloaked and policies hold up under pressure.

  • Cloaking validation: external scans must discover nothing
  • Entitlement and least-privilege policy testing
  • Performance, scale and failover verification
  • Behaviour on low-bandwidth and intermittently connected sites
  • Findings report with prioritised hardening actions

Our framework

How a session is secured, step by step

Every connection follows the same verified path. We design, build and test each step so access is granted only when identity, device and context all check out.

CLIENT CONTROL-LER IDENTITYPROVIDER GATEWAY(PEP) APPAPPAPP SPA knockIdentity and contextmTLS to Gatewaycloaked until verified
1

Single packet authorization

The client sends an access request to the Controller using SPA.

2

Context check

The Controller verifies identity and context, then returns a live entitlement.

3

Entitlement upload

The client presents the entitlement to the Gateway, which reveals only matching applications.

4

Segment of one

A dynamic, per-session network segment is built for that user.

5

Continuous monitoring

Context is watched constantly and the segment adapts as conditions change.

Use cases

One platform, many access scenarios

The same policy engine covers people, services and devices across every environment you run.

Secure remote access

Replace VPN with fast, individual tunnels for every remote user.

Server-initiated connectivity

Support management, scanning and helpdesk flows that start from the server side.

Branch and site connectivity

Secure site-to-site and branch access without a shared tunnel.

OT and IoT access

Protect legacy workloads and devices that cannot run an agent.

SaaS application access

Give trusted users and devices controlled access to SaaS.

Workload-to-workload

Apply the same policy to service communication across clouds and data centers.

Architecture

Direct-routed versus cloud-routed ZTNA

How AppGate positions its architecture against cloud-routed models.

AppGate direct-routedCloud-routed (typical)
Traffic pathDirect mTLS from device to GatewayAll traffic through a vendor cloud broker
On-premises usersStay on the corporate networkOften hair-pinned via the internet
TunnelsIndividual, high-performance tunnelsShared tunnels, double encryption
Protocol supportFull range, including VoIP and server-initiatedProxy design can limit protocols
ControlDecisions inside your boundaryDependent on vendor cloud trust
Cost profileFewer appliances, smaller footprintAdded bandwidth and licensing charges

Performance and assurance

Built for demanding environments

Vendor-reported results for large-scale deployments, backed by independent certifications and designs for sovereign and disconnected networks.

8-10xBetter performance than cloud-routed ZTNA
5xFewer appliances in large-scale environments
10xSmaller CPU and RAM footprint
$10M+Annual savings in very large deployments
NIAP Protection ProfileCommon CriteriaFIPS 140-3Sovereign deploymentsAir-gapped designsLow-bandwidth and disconnected sitesData-centric policyPolicy as code

Ecosystem

Fits the environments you already run

Protect applications and resources wherever they live, and tie policy into your identity and DevOps tooling.

On-premisesAWSAzureGoogle CloudSaaSBranch and IoT / OTIdentity providersDevOps and GitOps

Our approach

A proven delivery methodology

Clear stages, defined deliverables and sign-off at every step.

1. AssessMap users, applications, VPN usage and risk.
2. DesignDefine the access model, policies and topology.
3. ImplementDeploy, migrate in phases and automate policy.
4. ValidateProve cloaking, test least privilege and hand over.

Why Trezbon

Independent, regional and security-first

Delivery from Dubai across the UAE and wider GCC, with design choices that respect data-sovereignty requirements.

Architecture-led

We start from your risks and applications, then design the access model, not just install a product.

Low-disruption migration

Phased VPN replacement with parallel running keeps users productive throughout.

Tested and documented

Every engagement ends with test evidence, as-built documentation and a hardening roadmap.

FAQ

AppGate professional services questions

Answers to common questions from security and network leaders.

Which AppGate professional services does Trezbon provide?

We cover the full lifecycle: Zero Trust access architecture and policy design, deployment of AppGate Controllers and Gateways across on-premises, cloud and hybrid environments, and validation testing of cloaking, entitlements and performance.

What is the difference between direct-routed and cloud-routed ZTNA?

In a direct-routed model the user's device builds an mTLS tunnel straight to the Gateway protecting the resource, so traffic does not detour through a vendor cloud. Cloud-routed models send traffic through a shared broker, which can add latency and cost and limits protocol support.

Can AppGate replace our VPN, and how disruptive is the migration?

Yes. AppGate is designed for VPN replacement and universal access for remote and on-premises users. We run a phased migration with a parallel-run period so users move group by group without disruption.

Does AppGate support sovereign or air-gapped deployments?

AppGate positions its direct-routed architecture as independent of any external cloud, with access decisions made inside your own security boundary. We design Controller and Gateway placement to meet data-sovereignty and isolation requirements.

How do I start an engagement?

Email info@trezbon.com or call +971-56146 5956. We scope the environment, agree deliverables and timelines, and issue a clear Service Description Document before work begins.

Ready to cloak your network?

Speak with a Trezbon specialist about AppGate design, deployment and testing for your environment.

Email info@trezbon.com