Menu
ServicesProductsAboutContact

Home / Services / Gigamon Professional Services

Gigamon logoProfessional Services

See every packet. Secure every path with Gigamon deep observability

Trezbon designs, deploys and validates the Gigamon Deep Observability Pipeline, giving your security and network tools complete, trustworthy visibility across data center, cloud and OT.

Request a ConsultationExplore Services
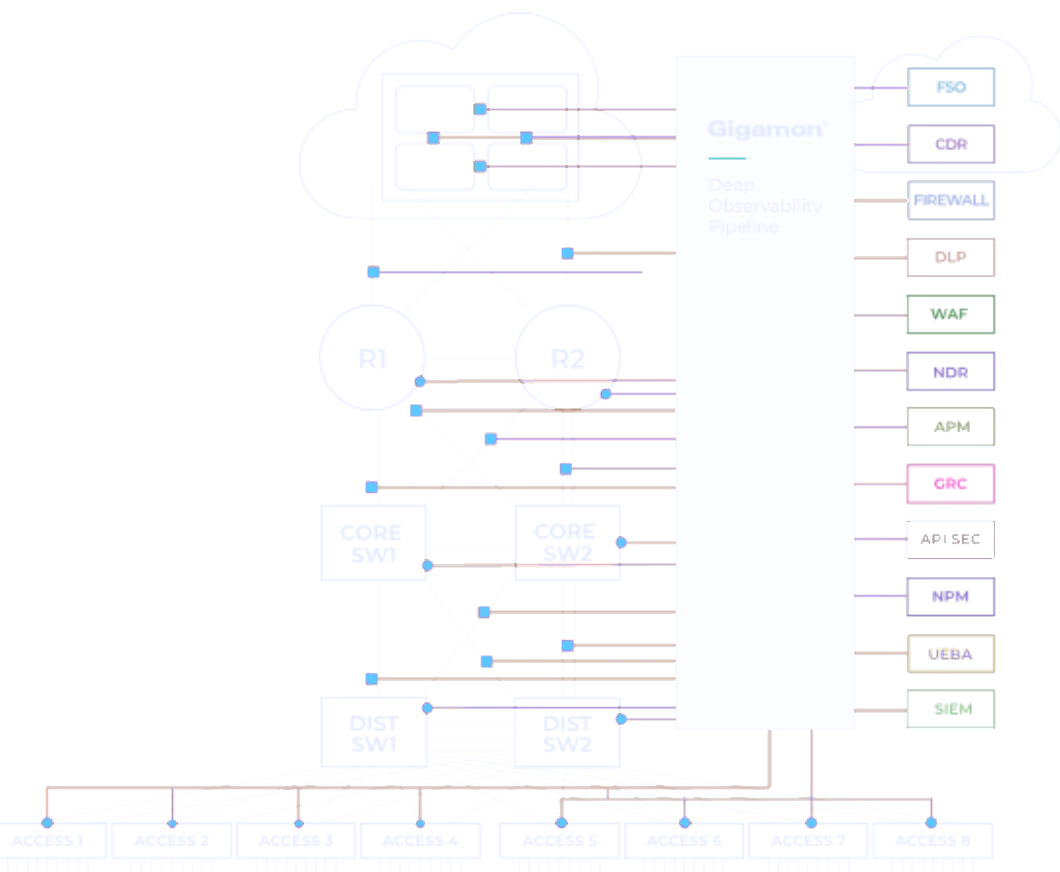
Gigamon Deep Observability Pipeline connecting routers, core, distribution and access switches, cloud workloads and security tools such as NDR, SIEM, DLP, WAF and firewalls
200+Integrated security and observability tools
10 of 10Top US federal agencies use Gigamon
Up to 50%Tool-cost reduction reported by Gigamon
95%Of MITRE C2 techniques visible

Figures as published by Gigamon (2024). Gigamon and the Gigamon logo are trademarks of Gigamon Inc.

Why deep observability

Visibility is the foundation of security, efficiency and agility

Logs can be spoofed and hosts can be compromised. The network tells the truth, and Gigamon turns it into clean, enriched data for every tool you run.

Help stop cyberthreats

Improve the effectiveness of the security tools you already run by feeding them complete, trustworthy network data.

Eliminate blind spots

Gain visibility across hybrid cloud, east-west traffic, encrypted flows and unmanaged devices.

Reduce IT and cloud cost

Send each tool only what it needs, raising tool capacity and lowering infrastructure spend.

What we deliver

End-to-end Gigamon professional services

One accountable team from visibility design to a validated, tool-ready pipeline.

01

Design

A visibility architecture built around your risks, tools and budget.

  • Blind-spot assessment across data center, campus, cloud and OT
  • Traffic-access plan: taps, agents, inline and out-of-band
  • Flow-mapping policy per tool: NDR, SIEM, IDS, APM, NPM
  • Decryption strategy: inline, passive or Precryption
  • Sizing, bill of materials and cost model
02

Implementation

Controlled deployment of the Gigamon Deep Observability Pipeline.

  • Physical visibility nodes and passive taps
  • Virtual and cloud taps with V Series processing
  • De-duplication, slicing, filtering and sampling policies
  • TLS decryption and 1-to-1 NetFlow/IPFIX generation
  • Tool onboarding and cutover with minimal disruption
03

Testing

Proof that every tool sees the right traffic before go-live.

  • Traffic-map, packet-loss and tool-feed validation
  • Decryption and metadata enrichment checks
  • Inline bypass and failover testing
  • Detection use cases: lateral movement, C2, SSH on port 443
  • Findings report with optimisation and tool-offload savings

Our framework

The Trezbon deep observability delivery framework

Network packets are accessed, transformed, enriched and brokered to each tool. We design and tune every stage so your tools receive exactly the data they need.

Public cloudData centerVirtual / privateOT / IoTACCESSTap andaggregateTRANSFORMFilter, dedupe,decryptENRICHAdd networkmetadataBROKERDeliver toeach toolNDRIDSSIEMDLPPCAPNPMNETWORK PACKETS INENRICHED DATA OUT

Security objectives

Outcomes we engineer for

Every engagement is tied to a business objective, not just a deployment checklist.

Cyberthreat protection

  • Unmanaged devices
  • Lateral movement
  • Command and control

Response and recovery

  • MTTR improvement
  • Dwell-time reduction
  • Scope, origin, impact

Standards and compliance

  • PCI DSS, DORA, CMMC
  • Zero Trust, M-21-31
  • NIST, ISO 27001, NIS2

Business modernization

  • Cloud migration
  • DevOps initiatives
  • NetFlow offload from devices

Cost optimization

  • Tool optimization
  • Noise reduction
  • Cloud NDR savings

Standards and compliance

Visibility that supports your frameworks

Source-of-truth network data helps meet logging, encryption-monitoring and zero trust requirements. Coverage below reflects Gigamon's own control mapping.

56DoD Zero Trust controls addressed
25PCI risk controls addressed
53CMMC practices with primary or enhanced visibility
82MITRE ATT&CK techniques with primary or enhanced visibility
MITRE ATT&CKDoD Zero TrustNIST CSFISO 27001NIST 800-53PCI DSSSOXCMMCHIPAA / HITRUSTSOC 2DORANIS2GDPRM-21-31

Cloud and virtual visibility

Consistent visibility from data center to multi-cloud

Pair Gigamon with cloud NDR and SIEM tools, with encrypted visibility through Precryption and one consistent experience across cloud and on-premises.

AWSAzureGoogle CloudVMwareNutanixOpenStackKubernetes

Cloud mirroring cost per GB (AWS example)

AWS default mirroring0.75¢ / GB
GigaVUE Cloud Suite~0.10¢ / GB

Gigamon model for AWS US West, including tapping, transport, compute and licence cost. Actual savings vary by environment.

Ecosystem

Works with the tools you already own

Gigamon feeds 200+ tools across these categories, so we design around your current investments instead of replacing them.

NDRIDSCAASMNACDLPSIEMObservabilityPCAPAPMNPMAIOps

Our approach

A proven delivery methodology

Clear stages, defined deliverables and sign-off at every step.

1. AssessMap blind spots, tools, traffic and constraints.
2. DesignProduce the visibility architecture and tool-feed plan.
3. ImplementDeploy taps, nodes and policies with controlled cutovers.
4. ValidateTest detections, prove savings and hand over.

Why Trezbon

Independent, regional and lifecycle-focused

Design around your tools and risks, with delivery from Dubai across the UAE and wider GCC.

Tool-agnostic design

Feeds are shaped around your NDR, SIEM, IDS and APM stack, not a fixed bundle.

Security and network fluency

Our engineers bridge network architecture and security operations, where visibility projects succeed or stall.

Documented and validated

Every engagement ends with test evidence, as-built documentation and a clear optimisation path.

FAQ

Gigamon professional services questions

Answers to common questions from security and network leaders.

Which Gigamon professional services does Trezbon provide?

We cover the full lifecycle: visibility design, deployment of the Gigamon Deep Observability Pipeline across physical, virtual and cloud environments, and validation testing of traffic maps, decryption and tool feeds.

Which environments can you cover?

Data center, campus and OT networks, virtual platforms such as VMware, Nutanix, OpenStack and Kubernetes, and public clouds including AWS, Azure and Google Cloud.

Will it work with the security and monitoring tools we already own?

Gigamon integrates with 200+ security, visibility and observability tools, including NDR, IDS, SIEM, DLP, NAC, APM, NPM and packet-capture platforms. We design feeds around your existing stack.

Can Gigamon visibility help with compliance?

Network-derived visibility supports frameworks such as PCI DSS, DORA, CMMC, NIS2, NIST and Zero Trust architectures. We map the visibility you need to your control requirements; formal certification remains with your auditors.

How do I start an engagement?

Email info@trezbon.com or call +971-56146 5956. We scope the environment, agree deliverables and timelines, and issue a clear Service Description Document before work begins.

Ready to eliminate your network blind spots?

Speak with a Trezbon specialist about Gigamon design, deployment and testing for your environment.

Email info@trezbon.com